 Ali Ikhwan
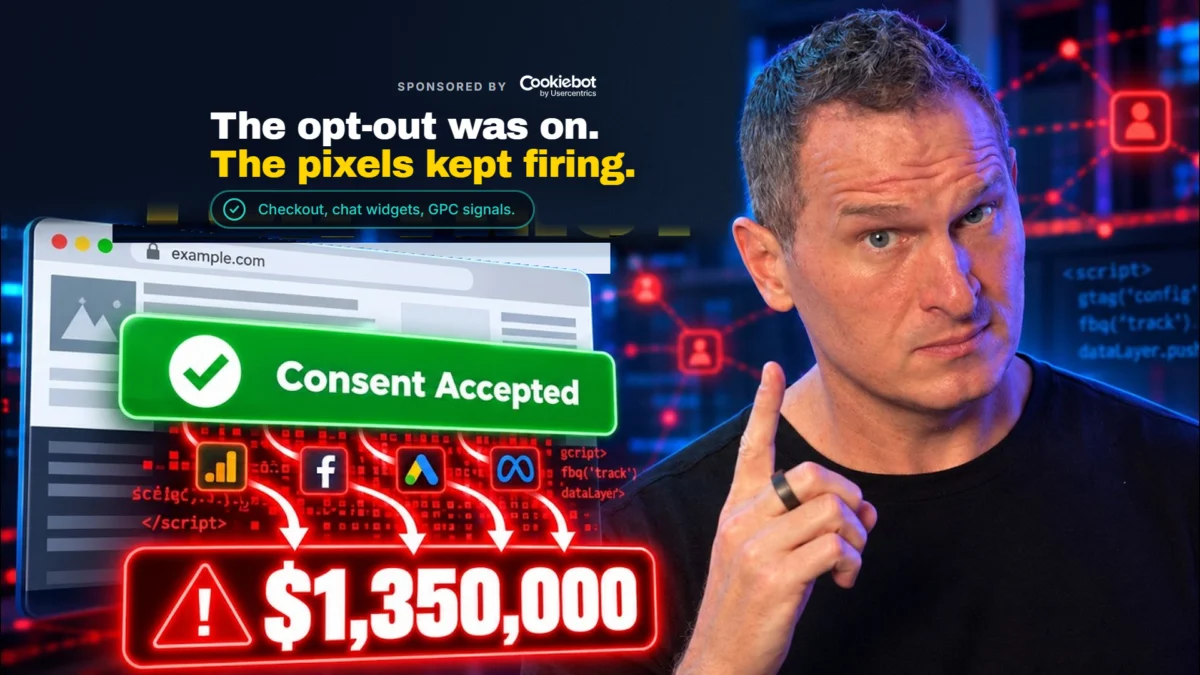
The California Privacy Protection Agency (CPPA) has issued a landmark $1.35 million fine against Tennessee-based retailer Tractor Supply, marking a significant escalation in the enforcement of the California Consumer Privacy Act (CCPA). The penalty, finalized in September 2025, represents one of the largest fines ever levied by the agency and serves as a stark warning to national corporations that privacy compliance requires more than just the presence of a "cookie banner."
The investigation into Tractor Supply originated from a single consumer complaint rather than a broad regulatory sweep or a class-action lawsuit. This individual grievance triggered a comprehensive audit of the company’s digital infrastructure, revealing systemic failures in how the retailer handled user data and opt-out requests. The case underscores a growing trend among state regulators to hold companies accountable for the technical efficacy of their privacy tools, rather than just their stated policies.
The Mechanics of Non-Compliance: Where Tractor Supply Erred
The CPPA’s investigation identified four primary areas where Tractor Supply’s implementation of privacy protections failed to meet legal standards. Despite having a visible consent management platform, the underlying technology did not consistently honor the choices made by users.
First, the agency found that Tractor Supply failed to honor Global Privacy Control (GPC) signals. GPC is a browser-level setting that allows users to broadcast a "do not sell or share" preference to every website they visit. Under California law, websites are required to recognize and respect these signals automatically. Tractor Supply’s system reportedly ignored these signals, continuing to track users who had already expressed a desire for privacy through their browser settings.
Second, the investigation revealed that even when users manually opted out via the website’s on-screen banner, tracking pixels from third-party advertising platforms continued to fire. This discrepancy between the user’s choice and the site’s technical execution is often referred to as "consent leakage," where marketing scripts bypass the consent management layer.

Third, the company was cited for failing to provide a "clear and conspicuous" link for users to opt out of the sale or sharing of their personal information. Finally, the CPPA noted that the retailer’s privacy policy was insufficient, failing to accurately describe how consumer data was being processed and shared with third-party vendors.
Beyond the financial penalty, the settlement requires Tractor Supply to undergo regular, third-party audits of its tracking technologies. This mandate highlights the agency’s focus on long-term technical accountability rather than one-time corrective actions.
A Growing Pattern of Multi-State Enforcement
The Tractor Supply case is not an isolated incident but part of a broader, more aggressive enforcement landscape. While California remains the most active jurisdiction, privacy litigation is expanding across the United States as more than 20 states have now enacted or implemented comprehensive privacy laws.

In July 2025, TicketNetwork reached an $85,000 settlement with the Connecticut Attorney General, marking the first monetary penalty under Connecticut’s Data Privacy Act. The issue mirrored the Tractor Supply case: the company’s privacy rights mechanisms were either misconfigured or entirely non-functional.
The momentum continued into early 2026. In February, Disney settled with the California Attorney General for $2.75 million following allegations that its opt-out mechanisms were fragmented. According to the complaint, when a user opted out on one device or service, the preference was not synchronized across the user’s entire account, leading to unauthorized data sharing on other platforms.
Shortly thereafter, in March 2026, the CPPA fined PlayOn Sports $1.1 million. The agency cited a lack of effective opt-out methods and a failure to honor browser-based privacy signals, further cementing GPC compliance as a top priority for regulators.

Chronology of Major US Privacy Enforcement Actions (2025–2026)
- July 2025: TicketNetwork pays $85,000 to Connecticut for misconfigured privacy rights mechanisms.
- September 2025: Tractor Supply is fined $1.35 million by the CPPA for GPC failures and "leaky" consent banners.
- February 2026: Disney reaches a $2.75 million settlement over fragmented, device-specific opt-out failures.
- March 2026: PlayOn Sports is penalized $1.1 million for failing to implement effective opt-out tools and ignoring GPC signals.
These cases demonstrate that regulators are no longer satisfied with "checked box" compliance. They are increasingly employing technical specialists to verify that data flows actually stop when a consumer clicks "decline."
Technical Analysis: Why Consent Systems Fail
The disconnect between a website’s front-end banner and its back-end data processing is frequently a result of technical complexity rather than intentional negligence. For measurement and marketing teams, consent usually breaks in three specific areas:
1. Isolated Checkout Environments
Many e-commerce platforms utilize third-party checkout systems or legacy subdomains that operate independently of the main site’s script management. While the homepage may have a robust consent banner, the checkout page—where the most sensitive consumer data is often collected—may load tracking pixels that never receive the "opt-out" signal from the initial landing page.

2. Third-Party Widgets and "Shadow IT"
Chat widgets, support bubbles, and social media embeds often function as "mini-applications" within a website. These widgets frequently load their own third-party scripts. If these scripts are not integrated into the site’s central Consent Management Platform (CMP), they continue to collect and transmit data regardless of the user’s privacy settings.
3. Downstream Data Integration
The modern marketing "stack" is a chain of interconnected services. When a user opts out, that signal must travel from the browser to the Tag Manager, and subsequently to the server-side analytics, the CRM, and the advertising platforms. If any link in this chain is broken, the data continues to flow to vendors, creating a liability for the first-party site owner.
The Shift Toward Google Consent Mode and Server-Side Solutions
In response to the rising risk of fines, many organizations are moving away from "Basic" consent implementations toward more sophisticated models. A primary example is Google Consent Mode, which allows tags to adjust their behavior based on the user’s consent status.

In "Basic Consent Mode," tags are hard-blocked until a user provides affirmative consent. While this ensures compliance, it often results in a total loss of data for a significant portion of the audience. Conversely, "Advanced Consent Mode" allows tags to load in a restricted state even if consent is denied. In this state, the tags send "cookieless pings" to Google’s servers. These pings do not contain personal identifiers but provide enough aggregate data for platforms to use machine learning to model conversions and behavior.
Furthermore, server-side tagging has emerged as a preferred method for maintaining control. By routing all data through a first-party server before it is dispatched to third-party vendors, companies can "sanitize" data or block transmissions based on the consent signals received. However, legal experts warn that server-side tagging is a tool for management, not a loophole for compliance. The fundamental requirement remains the same: the user’s choice must be honored throughout the entire ecosystem.
Industry Implications and the Path Forward
The Tractor Supply fine marks a turning point for the retail and digital marketing industries. It highlights that being headquartered outside of California does not provide immunity from its stringent privacy laws if a company serves California residents.

Marketing and measurement teams are now being tasked with conducting comprehensive audits that go beyond the surface level of the website. Industry analysts suggest that a robust audit must include:
- Verification of GPC signal detection.
- Mapping of all third-party scripts, particularly on checkout and account pages.
- Testing of "opt-out" persistence across different devices and sessions.
- Documentation of how consent signals are passed to downstream partners.
As Black Friday and the high-traffic holiday seasons approach, the pressure on retailers to ensure their "tracking pixels" are compliant has never been higher. The $1.35 million fine against Tractor Supply serves as a reminder that in the eyes of modern regulators, a broken opt-out button is just as much a violation as having no button at all.
The era of "set it and forget it" privacy banners has ended. For national retailers, the focus must now shift to technical verification, ensuring that the digital reality of their data processing matches the promises made in their privacy policies. As state agencies become more proficient at auditing code, the cost of technical negligence will likely continue to rise.

 Dwi Wanna