 Pevita Pearce
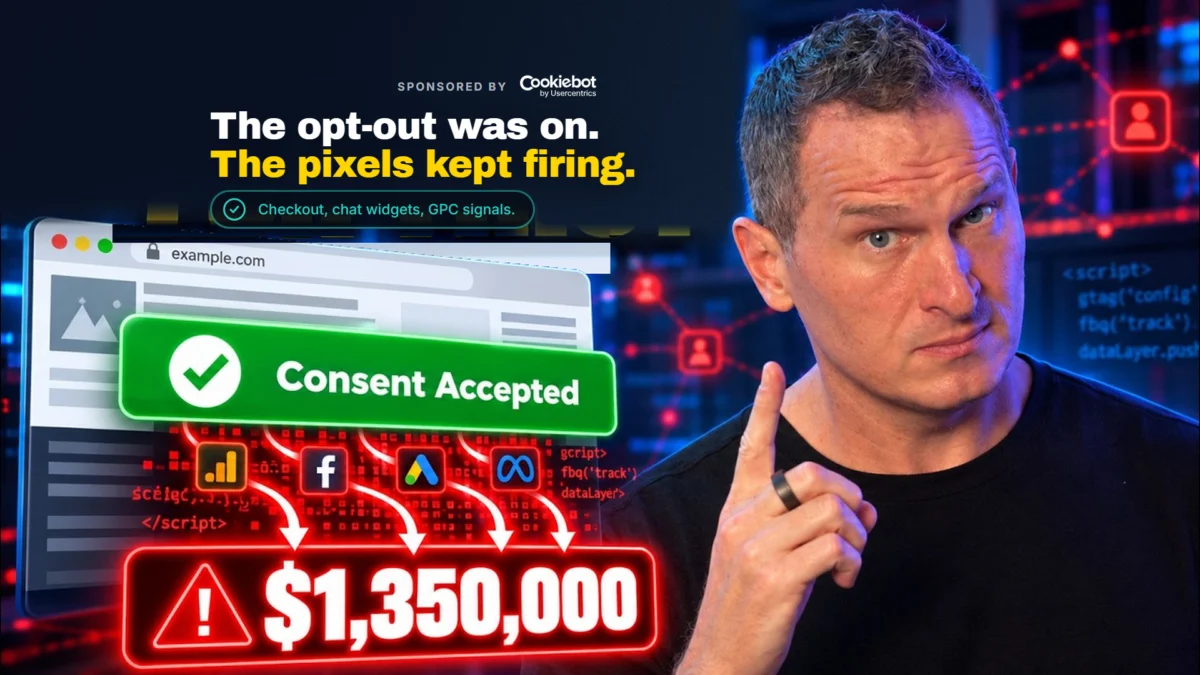
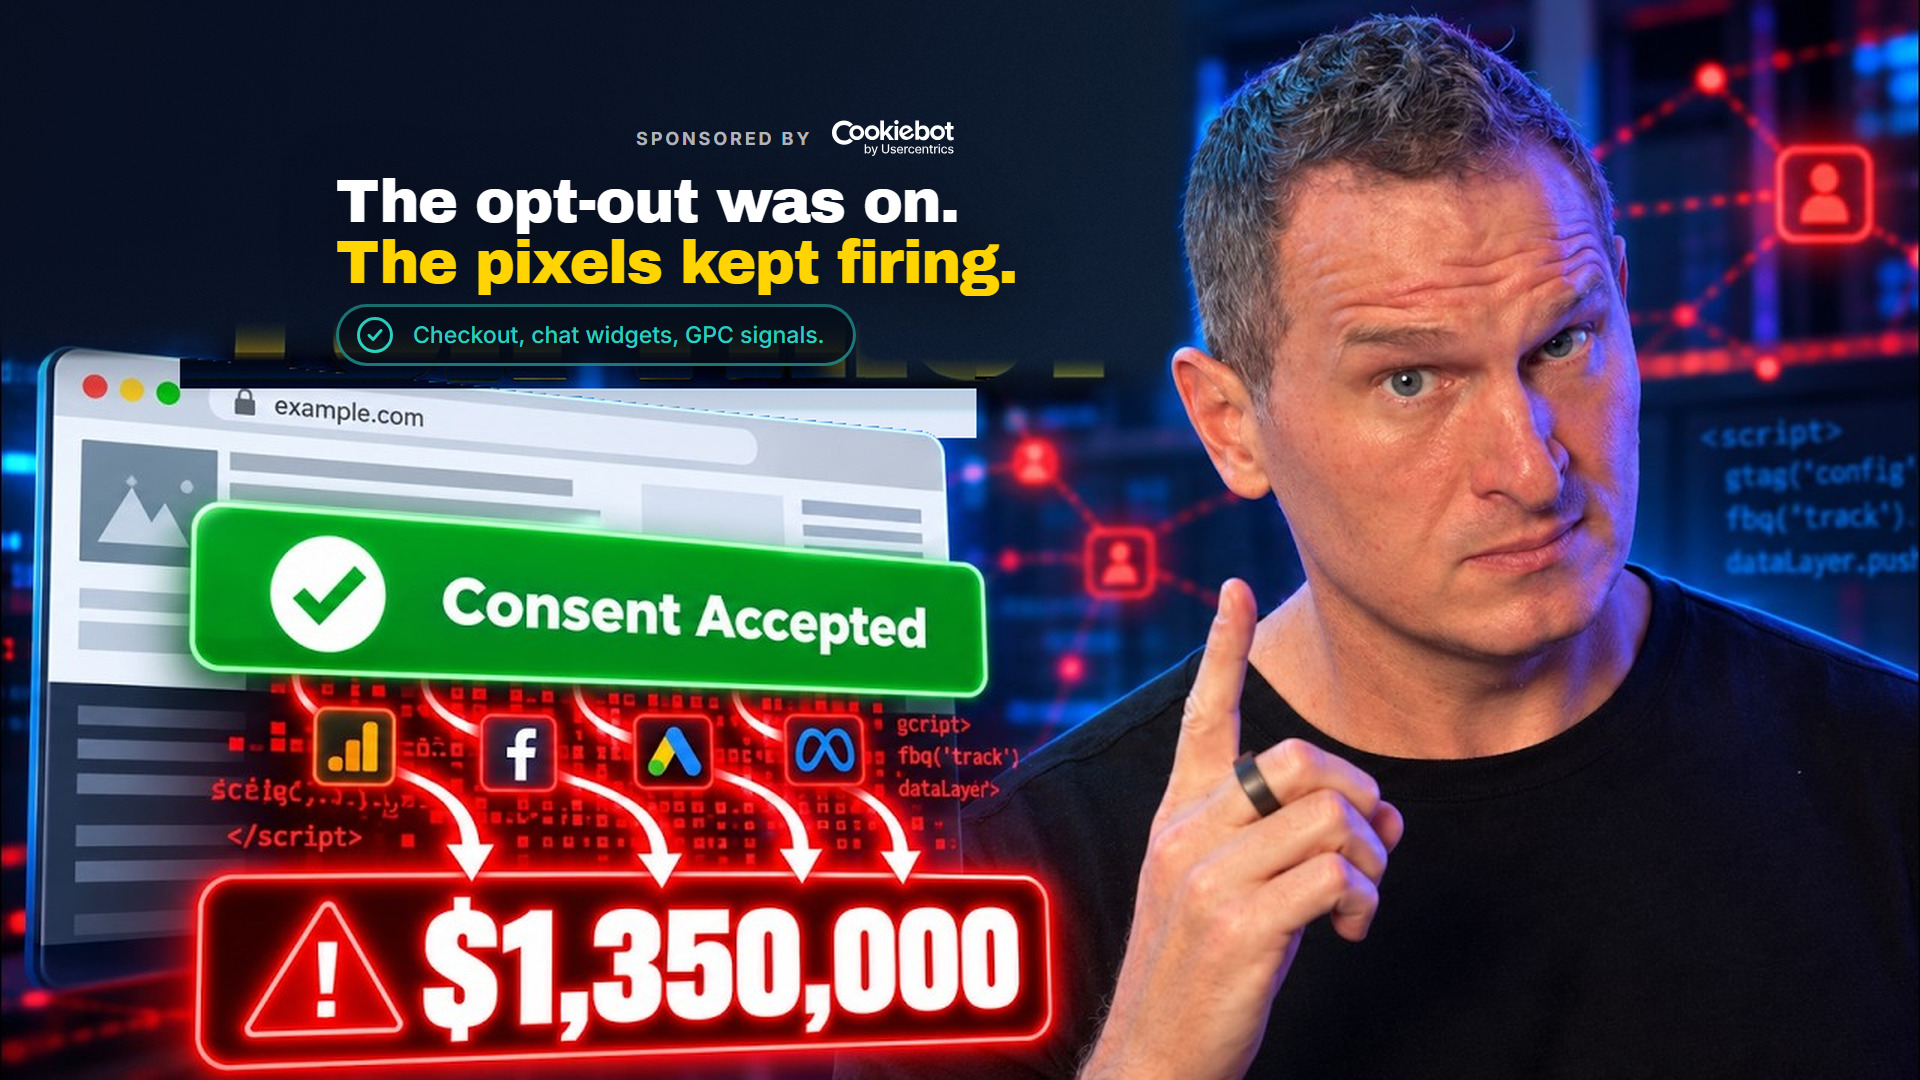
The California Privacy Protection Agency (CPPA) issued a landmark $1.35 million fine against Tractor Supply Company in September 2025, marking a significant escalation in the enforcement of state-level privacy regulations in the United States. The settlement, which stemmed from a single consumer complaint, highlights a growing trend of regulatory scrutiny regarding how corporations implement and honor digital consent. While the retail giant had established a visible consent management interface, investigators discovered that the underlying technical infrastructure failed to stop tracking pixels from firing after users opted out, and the system did not recognize browser-level privacy signals. This case serves as a critical precedent for the retail and marketing industries, demonstrating that the mere presence of a cookie banner does not constitute legal compliance if the technical execution is flawed.
The Catalyst and Investigation
The enforcement action against Tractor Supply began not with a broad regulatory sweep or a class-action lawsuit, but through an individual consumer’s grievance filed with the CPPA. This individual noticed that despite interacting with the website’s opt-out mechanisms, their data continued to be transmitted to third-party advertising platforms. Upon receiving the complaint, the CPPA launched an investigation into the company’s digital data practices under the California Consumer Privacy Act (CCPA) and the California Privacy Rights Act (CPRA).
The investigation revealed that Tractor Supply’s privacy failures were systemic rather than incidental. The agency identified four primary violations: the continued firing of tracking pixels after a consumer had explicitly opted out; the failure to honor Global Privacy Control (GPC) signals; inadequate disclosures within the privacy policy regarding the sale or sharing of personal information; and the absence of required service provider contracts with third-party vendors. As part of the settlement, Tractor Supply was not only required to pay the $1.35 million penalty—the largest issued by the agency at that time—but also to submit to regular third-party audits of its tracking technologies to ensure ongoing compliance.

A Chronology of Privacy Enforcement (2025–2026)
The Tractor Supply settlement was part of a broader wave of enforcement actions across various jurisdictions, signaling a shift from educational grace periods to strict financial penalties. In July 2025, TicketNetwork reached an $85,000 settlement with the Connecticut Attorney General, representing the first monetary penalty under the Connecticut Data Privacy Act (CTDPA). The violation involved misconfigured privacy rights mechanisms that prevented users from exercising their legal rights.
In early 2026, the California Attorney General announced a $2.75 million settlement with Disney. The core of the Disney case involved "siloed" opt-outs; when a user opted out of tracking on one device or service, the company failed to apply that preference across the user’s entire account or ecosystem. Shortly thereafter, in March 2026, PlayOn Sports was fined $1.1 million by the CPPA for failing to provide an effective opt-out method and for ignoring GPC signals. This timeline demonstrates that regulatory bodies are increasingly focusing on the "interoperability" of consent—ensuring that a user’s choice is respected across all platforms and through all automated signals.

Technical Analysis of Consent Failure
The Tractor Supply case underscores the "technical debt" many companies face when integrating modern privacy requirements into legacy web architectures. Analysts point to several specific areas where consent chains typically break.
The Global Privacy Control (GPC) Mandate
One of the most significant technical requirements highlighted in recent fines is the Global Privacy Control. GPC is a browser-level setting that allows users to broadcast a "do not sell or share" signal to every website they visit automatically. Under California law, honoring this signal is mandatory. Many organizations rely on Consent Management Platforms (CMPs) to handle these signals, but if the CMP is not correctly integrated into the site’s header, or if certain scripts load before the CMP initializes, the GPC signal is effectively ignored. In the cases of Tractor Supply and PlayOn Sports, the failure to recognize GPC was cited as a primary violation.

The "Broken Chain" in Downstream Data Flows
Consent is often captured at the front end (the cookie banner) but fails to propagate to the back end. On many e-commerce sites, checkout pages and chat widgets operate on different subdomains or third-party platforms. If the consent signal collected on the homepage does not travel to these auxiliary services, tracking pixels may fire on the most sensitive parts of the customer journey—such as the completion of a purchase—even after a user has opted out.
Furthermore, "downstream integrations" present a significant risk. When a visitor opts out, that preference must be communicated to every vendor in the stack, including analytics providers, CRM systems, and social media advertising pixels. If the tracking system is not configured to "pause" or "anonymize" data based on the consent string, the organization remains liable for the unauthorized sharing of data.

The Role of Google Consent Mode and Data Modeling
As companies move to correct these failures, many are turning to advanced technical solutions like Google Consent Mode to balance compliance with data utility. There is a distinct difference between "Basic" and "Advanced" implementations of these tools.
Under a "Basic" consent mode, all tags are blocked until the user provides affirmative consent. While this ensures total compliance, it results in a total loss of data for opted-out users, creating significant gaps in marketing attribution and site performance metrics.

"Advanced" consent mode, however, allows tags to load in a restricted state even if consent is denied. In this state, the tags do not read or write cookies but instead send "cookieless pings" to the server. These pings contain functional information (such as the device type and conversion type) without identifying the user. This data allows platforms like Google Analytics 4 to use machine learning to model the behavior of opted-out users, providing companies with estimated conversion data while strictly adhering to the user’s privacy choice. The Tractor Supply fine suggests that the legal risk lies not in the collection of data itself, but in the collection of identifiable data against a user’s expressed wishes.
Broader Impact and Industry Implications
The $1.35 million fine serves as a warning that privacy compliance is no longer a "set and forget" task for IT departments. The legal landscape in the United States is rapidly fragmenting, with over 20 states having passed or enacted comprehensive privacy laws as of late 2025. Each of these laws, from Virginia’s VCDPA to Colorado’s CPA, carries its own nuances regarding opt-out rights and the definition of "sensitive data."

The implications for the 2025 holiday shopping season and beyond are significant. Retailers are now forced to conduct comprehensive audits of their "martech" (marketing technology) stacks to ensure that every script, from third-party chat bubbles to affiliate tracking pixels, respects the central consent signal.
Industry experts suggest a three-pronged approach for maintaining compliance:

- Technical Verification: Moving beyond the visual interface of the cookie banner to verify that network requests are actually suppressed when consent is denied.
- GPC Integration: Ensuring that the website’s architecture is capable of detecting and responding to browser-level signals before any tracking scripts are executed.
- Contractual Rigor: Implementing the required service provider contracts with all third-party vendors to ensure that data shared for functional purposes is not repurposed for independent advertising use.
Conclusion
The Tractor Supply enforcement action represents a turning point in the maturity of U.S. privacy law. It demonstrates that regulatory agencies have developed the technical sophistication to look behind the "veneer" of compliance—the cookie banner—and investigate the actual movement of data. For modern enterprises, the cost of a technical misconfiguration in a consent string now carries a million-dollar price tag. As state agencies continue to respond to individual consumer complaints with full-scale investigations, the priority for digital businesses has shifted from simple data collection to the rigorous, verifiable management of consumer choice. The Tractor Supply case proves that in the eyes of the law, an illusory choice is no choice at all.

 Basiran