 Lina Irawan
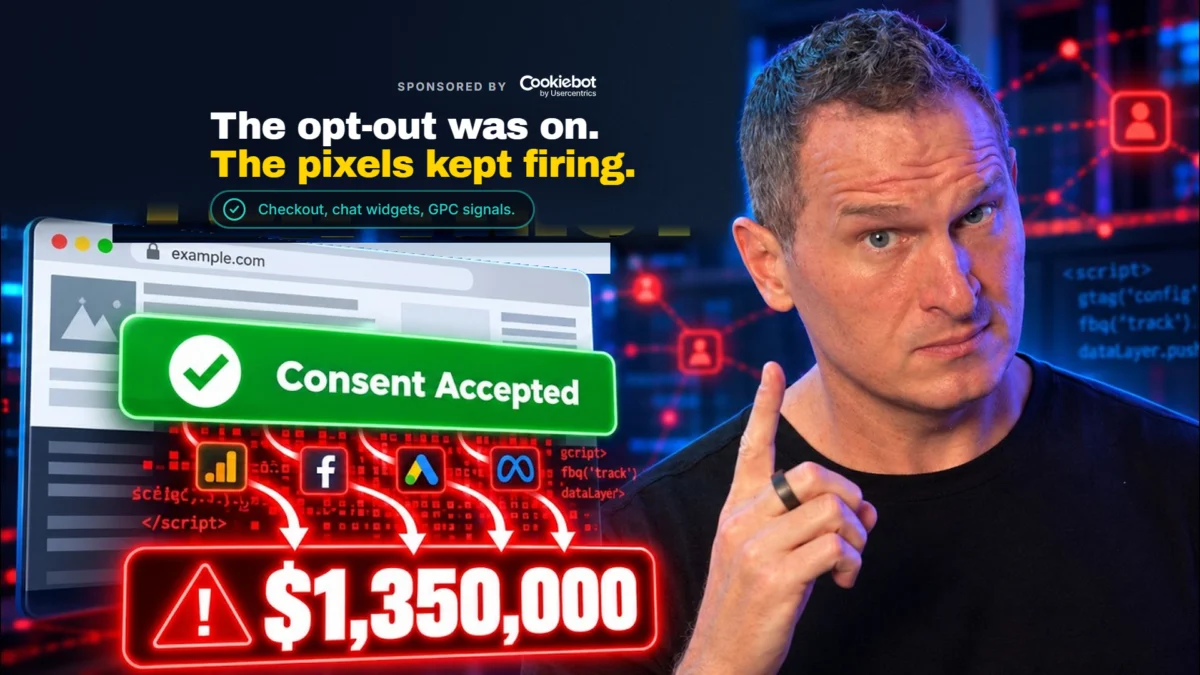
The digital marketing industry is currently navigating a pivotal shift in how consumer privacy is regulated and enforced. For years, many organizations operated under the assumption that implementing a visible cookie consent banner was sufficient to meet legal obligations. However, a series of high-profile enforcement actions, culminating in a landmark $1.35 million fine against Tractor Supply in September 2025, has shattered this "check-the-box" mentality. Regulators are moving beyond the surface level, scrutinizing the underlying technical architecture of websites to ensure that when a user opts out of tracking, the data transmission actually stops.
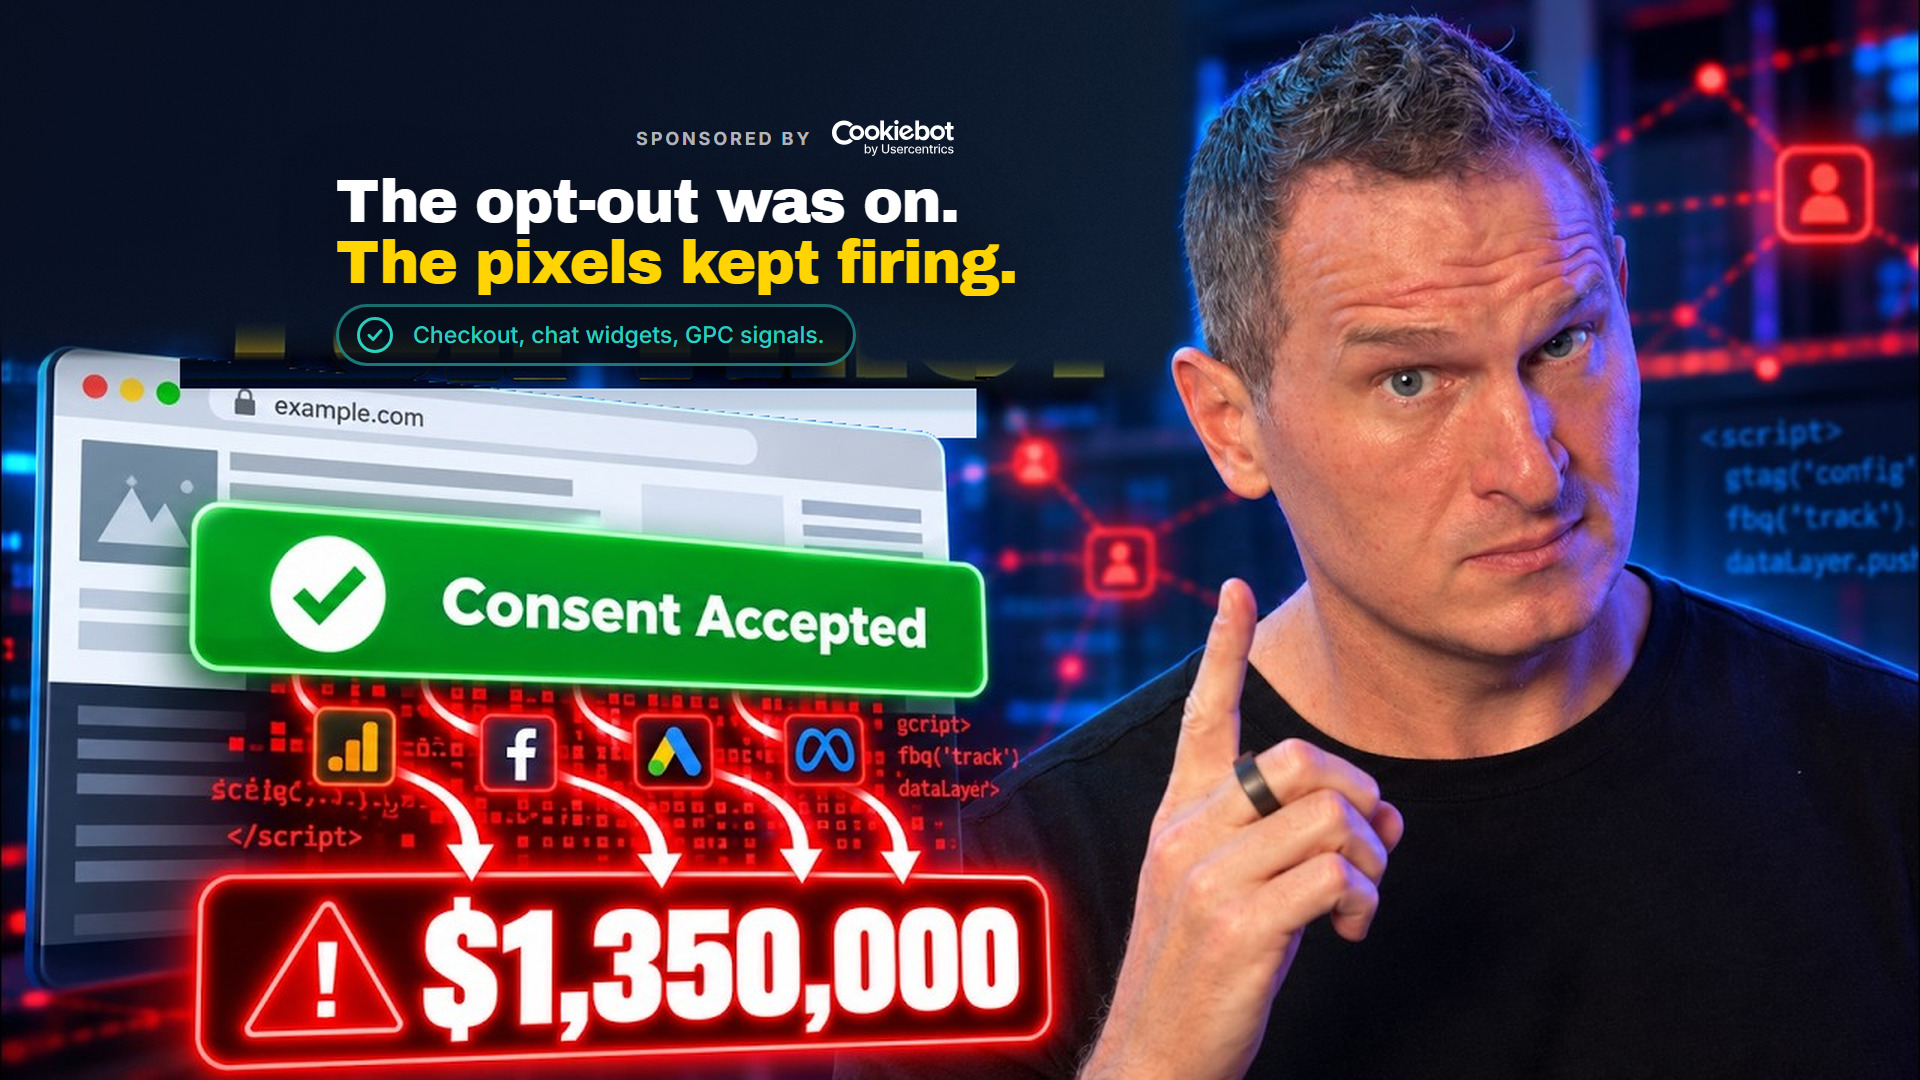
The Tractor Supply case serves as a stark warning for the retail and e-commerce sectors. The fine, issued by the California Privacy Protection Agency (CPPA), represents one of the largest penalties to date for violations of the California Consumer Privacy Act (CCPA). Perhaps most significantly, the investigation was not triggered by a massive data breach or a broad regulatory sweep, but by a single consumer complaint. This underscores a new reality: individual users are increasingly aware of their privacy rights and possess the tools to monitor whether companies are honoring their choices.
The Tractor Supply Settlement: A Breakdown of Technical Failures
The CPPA’s investigation into Tractor Supply revealed a significant disconnect between the company’s public-facing consent interface and its backend data practices. Despite having a consent banner in place, the agency identified four critical areas where the implementation failed to meet legal standards.

First, the investigation found that tracking pixels continued to fire and transmit data to third-party advertising platforms even after users had explicitly opted out via the website’s banner. This effectively rendered the user’s choice moot, as personal information continued to flow to ad tech vendors without authorization. Second, the company failed to honor Global Privacy Control (GPC) signals. GPC is a browser-level setting that allows users to broadcast a universal "do not sell or share" preference to every website they visit. Under California law, honoring these signals is mandatory, yet many organizations still lack the technical configuration to recognize them.
Third, the agency noted that the process for opting out was not sufficiently "clear and conspicuous." Regulators are increasingly targeting "dark patterns"—user interface designs that make it intentionally difficult for users to exercise their privacy rights. Finally, the settlement required Tractor Supply to submit to regular third-party audits of its tracking technologies. This move signals that regulators are no longer satisfied with self-certification; they are demanding verified proof of technical compliance.

A Growing Trend of Multi-State Enforcement
While California remains the vanguard of privacy regulation in the United States, the Tractor Supply case is part of a much broader national trend. Enforcement is no longer confined to the West Coast, as evidenced by a flurry of recent settlements across various jurisdictions.
In July 2025, TicketNetwork reached an $85,000 settlement with the Connecticut Attorney General. While the dollar amount was lower than the California cases, it was historically significant as the first monetary penalty issued under Connecticut’s specific privacy law. The core issue mirrored the Tractor Supply case: the company’s privacy rights mechanisms were either misconfigured or entirely non-functional, preventing users from successfully opting out of data sharing.

The momentum continued into early 2026. In February, Disney settled with the California Attorney General for $2.75 million. The Disney case highlighted a different but equally critical flaw: the "siloed" opt-out. Regulators found that when a user opted out on one device or specific service, the preference did not propagate across the user’s entire account or other connected devices. This "fragmented consent" is now a major focus for enforcement agencies who argue that a privacy choice should follow the identity of the consumer, not just the hardware they are using at a specific moment.
Shortly thereafter, in March 2026, the CPPA issued a $1.1 million fine against PlayOn Sports. Similar to the Tractor Supply findings, PlayOn Sports was cited for failing to provide an effective opt-out mechanism and for ignoring GPC browser signals. These cases collectively demonstrate that state attorneys general and dedicated privacy agencies are sharing strategies and focusing on the same technical vulnerabilities.

Identifying the Technical Blind Spots in Consent Management
For measurement and marketing teams, the primary challenge lies in the fact that consent often "breaks" in areas of the website that are not managed by the primary tag management system. There are several recurring "blind spots" where unauthorized tracking frequently occurs.
Disconnected Checkout Environments
E-commerce checkout pages are often built on different frameworks or hosted on separate subdomains for security reasons. Because of this architectural split, the consent signal captured on the homepage or product pages may not always "travel" to the checkout environment. If the checkout page loads its own set of marketing pixels—such as those for conversion tracking or cart abandonment—without checking the global consent status, a violation occurs.

Third-Party Chat and Support Widgets
Live chat tools are a frequent source of "rogue" scripts. These widgets often function as mini-applications within the site, loading their own third-party dependencies and cookies independently of the site’s main tag manager. Because these widgets are often implemented by customer service teams rather than technical marketing teams, they frequently bypass the organization’s standard consent protocols.
Downstream Data Orchestration
Compliance does not end at the browser. When a visitor opts out, that signal must be propagated through the entire data stack. If a website honors an opt-out on the front end but continues to send that user’s data to a Customer Relationship Management (CRM) system or a Data Management Platform (DMP) via a server-side feed, the company remains in violation of "sharing" restrictions. True compliance requires a unified "consent string" that travels with the data from the point of collection to every end-destination.

The Mandatory Nature of Global Privacy Control (GPC)
One of the most consistent themes in recent enforcement actions is the failure to recognize Global Privacy Control. GPC was developed as a response to "consent fatigue," allowing users to set their preference once at the browser level rather than interacting with a banner on every individual site.
For many organizations, the difficulty is that GPC is invisible. It is a signal sent in the HTTP header of the browser request. If a website’s Consent Management Platform (CMP) is not specifically configured to listen for this header, it will continue to load tracking scripts as if the user had no preference, right up until the user manually interacts with the on-site banner. Regulators have made it clear: the GPC signal is a legally binding request that takes precedence over the absence of a banner interaction.

Strategic Responses: Google Consent Mode and Server-Side Tagging
As the legal risks of non-compliance grow, companies are looking for technical solutions that balance privacy with the need for actionable marketing data. Two primary technologies have emerged as industry standards: Google Consent Mode and Server-Side Tagging.
Google Consent Mode: Basic vs. Advanced
Google Consent Mode allows tags to adjust their behavior based on the user’s consent status. Under "Basic" consent mode, tags are hard-blocked until consent is granted. This ensures total compliance but results in significant data gaps. "Advanced" consent mode offers a more nuanced approach. If a user denies consent, tags do not set cookies, but they send "cookieless pings" to Google’s servers. These pings contain non-identifying information like timestamp and browser type, which Google then uses to employ machine learning and model the conversions that would have otherwise been lost. This allows marketers to maintain a degree of measurement accuracy without violating the user’s privacy choice.
The Role of Server-Side Tagging
Server-side tagging shifts the data collection process from the user’s browser to a secure server owned by the company. This provides a "gatekeeper" layer where data can be cleaned, anonymized, or redacted before it is sent to third-party vendors. While server-side tagging is a powerful tool for data control, it is not a "loophole" for consent. If a user opts out, the server-side logic must be configured to stop the transmission of that user’s data just as strictly as a client-side script would.
Chronology of Major Privacy Enforcement (2025–2026)
To understand the current regulatory climate, it is helpful to view these events in chronological order, showing the rapid escalation of enforcement:

- July 2025: TicketNetwork fined $85,000 by the Connecticut Attorney General for non-functional privacy opt-out links. This marked the first financial penalty under the Connecticut Data Privacy Act (CTDPA).
- September 2025: Tractor Supply fined $1.35 million by the CPPA. The case highlighted the failure to honor GPC and the continued firing of pixels post-opt-out.
- February 2026: Disney settled for $2.75 million with the California AG. The focus was on the failure to provide a persistent, cross-device opt-out for logged-in users.
- March 2026: PlayOn Sports fined $1.1 million by the CPPA for lack of effective opt-out mechanisms and ignoring browser-level privacy signals.
Conclusion: The Shift Toward Technical Accountability
The $1.35 million Tractor Supply fine represents a turning point in the relationship between digital marketing and privacy law. It signals that the era of "cosmetic compliance"—where a banner exists but the underlying data flows remain unchanged—is over.
For businesses, the implications are clear: privacy is now a technical engineering requirement, not just a legal disclosure. Compliance must be verified through rigorous auditing of every script, every widget, and every downstream data feed. As more states adopt active privacy laws and as regulators become more technically sophisticated, the cost of "getting it wrong" will only continue to rise. Organizations that prioritize technical verification today will not only avoid the massive fines seen in 2025 and 2026 but will also build the long-term consumer trust that is becoming a competitive necessity in the modern digital economy.

 Lina Hope
 Asep Darmawan